December 15th, 2025 by ParadigmSI
By now, most of us are aware of the rising occurrence of ransomware-style cyber attacks. Malicious code is introduced into the enterprise through phishing or some other means, and propagated quickly to infect networks, servers, PC/laptops and other devices.
No organization is immune, and the threat is increasing each year. Large and small commercial companies, as well as state, local and federal governments have all fallen victim to attack. With ransomware, the goal of the cyber criminal is typically financial gain, but may also be an effective means for any other intention that can be used as leverage when your data and systems have been hijacked.
Like any other type of attacker scenario, the ideal victims are those organizations that have left themselves to be vulnerable as easy prey. Loss of access to IT systems and data can be devastating to the under-prepared. Intentional planning, preparedness and prevention are key to thwarting and mitigating these types of attacks.
For the enterprise organization, Disaster Recovery strategies need to be reviewed and updated as necessary to ensure full resiliency. Prevention techniques can begin with an assessment and review of Information Policies and Procedures. A posture review of the IT Systems and controls can be helpful, including timely server patching to stay current with security updates, implementation of proactive antivirus programs, as well as continuous monitoring and intrusion detection solutions.
Within the overall Business Continuity Management Strategy (BCMS) for the organization, it is imperative to identify the resiliency approach for all critical areas or asset classes. Typical assets to be managed for the organization include (but not limited to): Facilities, Personnel, IT/Systems, Data/Records, Supply chain, and Image/Reputation. The BCMS will need to address the “loss of asset” contingency for each of these areas.
In reality, ransomware can potentially affect all these areas, such as access to the Facility, ability for personnel to perform essential functions, management of the supply chain, and certainly loss of image and reputation. When it comes specifically to ransomware and DR strategies, IT/Systems and Data/Records are two of the key asset classifications that can be directly affected by such an attack.
In the case of critical Data/Records, if the primary site becomes infected with malware and you are locked out of these systems, does the organization have redundancy in place, in addition to failover strategies in order to be able to retrieve and operationalize this data? Does this include managed backups and offsite storage? Are these encrypted with full or incremental backups; scheduled hourly, daily or weekly? Are these aligned to the appropriate Recovery Point Objectives (RPOs) for the organization’s critical processes?
For IT/Systems, if the primary site becomes infected with malware and you are locked out of these systems, does the organization have redundancy and failover strategies in place that may include a geographically-dispersed cold-site, warm-site or hot-site? Are these aligned to the appropriate Recovery Time Objectives (RTOs) for the organization’s critical processes that depend on these systems? Depending on the RTO requirements and maximum tolerable downtime for critical processes in the organization, you may require an ‘Active-Active’ level resiliency for a near-real time failover capability as compared to an ‘Active-Passive’ DR strategy.
As sometimes this can be overlooked, be sure to also consider the backup and offsite storage of what is required to run these systems, such as employee pc-image profiles, server images, configuration files and copies of the required software programs with valid license keys.
Once all this is in place, how can you verify the effectiveness of your DR strategy, to include a possible ransomware attack? Many organizations will from time to time facilitate a tabletop exercise to simulate the response procedures for a disruption to the organization. This can be a good start, but be sure to simulate cascading failure scenarios that affect both operational processes as well as related IT/Systems and Data/Records, since most real life disruptions go beyond a single failure point.
Sometimes, instead of a simulated disruption, having a planned and scheduled outage disruption to actually shut down the primary IT systems and bring them back online in an organized manner can reveal the true Disaster Recovery readiness of the organization. Potential gaps will be revealed that may exist in a ransomware scenario when you have been shut out of all your primary IT Systems, programs and data.
The DR strategies required to mitigate against ransomware or any other type of disruption relies on having valid RTOs and RPOs for all the IT/Systems that support the organization. The Business Impact Analysis (BIA) will help you to identify these critical processes, resource and technology requirements, dependencies and operational RTOs and RPOs that will feed into the DR requirements. BC and DR plans can then be developed and documented, including the DR procedures for failover, recovery and restoration that may be needed during a malware or ransomware attack.
What is your level of confidence that you could successfully recover from a test of a primary systems shutdown, or from an actual malware attack? BC/DR planning tools like OpsPlanner™ can assist you and provide an effective foundation to build, plan, document, test, train, mature and continuously improve your organizational resiliency.
For more information about how to better prepare your organization with effective BC/DR Planning tools, or to schedule a tabletop exercise with our Certified Business Continuity Professionals, please contact us via:
- The contact form using the link at the top of this page
- Email at PSISales@ParadigmSI.com
- Call us at 800-558-9568 ext. 300
March 1st, 2025 by ParadigmSI
Implementing a Business Continuity Management Program
1. Establish the BCM Ownership.
2. Align BCM Program to organizational Strategic Goals.
3. Develop the BCM Policy.
4. Determine the BCM Strategy.
5. Determine the BCM Implementation Approach
The first step is to meet with decision-makers to understand and review the program approach, requirements and scope relative to implementation of the Business Continuity Management program.
The key focus is directed at identifying and then supporting the critical business functions.
Meet with decision-makers to understand and review the program approach, requirements and scope relative to OpsPlanner implementation for BCM/COOP.
Who? Decision-makers regarding the implementation factors for the continuity program (e.g. – IT representation for technology considerations; Agency-level BCM owners, etc..)
What is expected to be accomplished? Level-set on expectations and strategize operational decisions regarding specific implementation topics.
(e.g. – Who is required to approve a plan before it can be published?)
What distinct operational segments are covered in this program?
- Operational Groups:
- Lines of Business:
- Organizational Units:
- Locations: (Site -> Location)
- (named facilities: cold/hot sites? non-US sites? IS/failover locations? ancillary/support sites?
Define Critical Success Factors / Project Goals
For example:
- Identify gaps in RTO between business units and IT
- Accurately integrate information about people, contact information, locations, equipment and systems in a timely manner
- Allow business units to declare an event scenario and record the activities that occur for evaluation and improvement
- Document and test all BCP test plans
- Document and test all DR processes
Discuss desired implementation method:
- “Big Bang” approach: All Agencies brought online at one time, or
- Staged implementation, with lessons learned after initial deployment and period of operation.
Discuss desired training approach:
- “Train the trainer” –Individual focus sessions by user function? (e.g.: Admins, etc.)
Use internal or external staffing?
The first step in determining the BCM implementation approach is to decide if the BCM program will be implemented using internal/hired staff, or using external BCM consultants. Either approach can be valid, depending on the resource capabilities and budget that is available. Outsourcing the BCM program implementation to BCM Consultants can certainly streamline the process. If internal staff can lead and manage the BCM implementation, this can minimize third party expenses, but increase the amount of effort and expertise requirements from existing FTEs.
Manual, document-driven BCMP or software-based BCMP solutions?
In many cases the size of the organization and complexity of the BCM requirements will drive this decision. For other than very small organizations with minimal requirements, a software-based BCMP solution can be a great investment with positive return-on-investment.
There are many great BCM tools available in the marketplace. Certain features and capabilities can be tailored to certain industries and BCM requirements. It will be important to determine your key requirements and then review and assess which BCM tools best fit those organizational needs and requirements.
The OpsPlanner Business Continuity Planning Software solution can provide your organization with enterprise capabilities for Business Impact Analysis, Risk Assessment, Incident Management, and Automated Notification for a comprehensive Business Continuity Management program.
In addition, our Certified Business Continuity Planning Consulting professionals work shoulder-to-shoulder with you to facilitate enterprise-wide business continuity planning and participation, training, and support.
For more information about how to better prepare your organization with an effective Business Continuity Management System, please contact us via:
– The contact form using the link at the top of this page
– Email at PSISales@ParadigmSI.com
– Call us at 800-558-9568 ext. 300
Next up in Part 6: Initiate the BCM Program
March 1st, 2025 by ParadigmSI
Implementing a Business Continuity Management Program
1. Establish the BCM Ownership.
2. Align BCM Program to organizational Strategic Goals.
3. Develop the BCM Policy.
4. Determine the BCM Strategy.
5. Determine the BCM Implementation Approach.
6. Initiate the BCM Program
7. Business Impact Analysis
BIA Purpose
The Business Impact Analysis (BIA) is the critical first step in the conceptual transition from recovery to continuity. It is designed to establish a common understanding for endorsement by senior management, of what the enterprise sees as its key processes. It is the most important element, as well as the most complex component of the Business Continuity Planning (BCP) or Continuity Of Operations (COOP) program.
An effective BIA will:
Identify the processes or functions performed by an organization and the criticality of each process
Identify the resources required to support each process performed
Demonstrate interdependencies between processes and/or departments
Allow understanding of the impact of failing to perform a key process
Assign a Recovery Time Objective (RTO) for each process and a Recovery Point Objective (RPO)
Identify Recovery Requirements
Prioritize the order in which the business units will recover
The BIA will assign priorities to those processes and the quantified impact on the organization should the processes be disrupted, serve to determine vulnerabilities based on the failure of critical functions, and ascertain which functions are mission-critical, critical, essential, or non(less)-essential.
To begin the BIA Process:
Develop detailed project plans for implementation of the BIA
Form a BIA Steering Committee
Identify the BIA Administrator Team
Conduct a Project Kickoff Session and invite Project Stakeholders
For more detailed information about how to perform a Business Impact Analysis, better prepare your organization with effective BC/DR Planning tools, or to schedule a tabletop exercise with our Certified Business Continuity Professionals, please contact us via:
The contact form using the link at the top of this page
Email at info@ParadigmSI.com
For more information, call us at 800-558-9568 ext. 300
To speak with a Sales Representative about Business Continuity Planning Consulting or Business Continuity Software, please call:814-330-2560
Next up in Part 8: Risk Analysis
February 25th, 2025 by ParadigmSI
Implementing a Business Continuity Management Program
1. Establish the BCM Ownership.
2. Align BCM Program to organizational Strategic Goals.
3. Develop the BCM Policy.
4. Determine the BCM Strategy.
5. Determine the BCM Implementation Approach.
6. Initiate the BCM Program
7. Business Impact Analysis
8. Risk Analysis
The Risk Analysis involves a determination of the events that can adversely affect an organization, the damage such events can cause and the controls needed to prevent or minimize the effects of potential loss. Risks can be quantified by determination of: Potential Threats, Probabilities, Impacts and Vulnerabilities.
The Risk Analysis will:
– Identify potential threats,
– Understand threat size impacts
– Determine mitigation techniques for each threat,
– Perform cost/benefit analysis for each mitigation technique,
– Prioritize/summarize viable & effective mitigation strategies,
– Implement mitigation strategies using: avoidance (eliminate), reduction (mitigate), transference (outsource/insure), retention (accept/budget)
Risk Assessment Strategies will focus on:
Preemptive/preventative measures to reduce the risk or impact of a risk event
Approaches to continuing/resuming key business process activities during a crisis (e.g., executing key processes remotely, utilize additional working shifts).
The developed strategies will be quantified in terms of cost/benefit, with final selection of strategies for implementation by the Risk Management Committee.
For each risk develop strategies that enhance business continuity of the process. Strategies will outline approaches to either:
Increase the level of control associated with the process, and/or
Decrease the business impact associated with a process disruption.
Where not covered already develop strategies to secure the availability of “Mission Critical Resources”. Develop a timeline to implement the suggested strategies and submit to management for approval.
For more detailed information about how to perform a Risk Analysis, better prepare your organization with effective BC/DR Planning tools, or to schedule a tabletop exercise with our Certified Business Continuity Professionals, please contact us via:
The contact form using the link at the top of this page
Email at PSISales@ParadigmSI.com
For more information, call us at 800-558-9568 ext. 300
To speak with a Sales Representative about Business Continuity Planning Consulting or Business Continuity Software, please call: 814-330-2560
Next up in Part 9: Plan Development
May 23rd, 2023 by ParadigmSI
Implementing a Business Continuity Management Program
1. Establish the BCM Ownership.
2. Align BCM Program to organizational Strategic Goals.
3. Develop the BCM Policy.
4. Determine the BCM Strategy.
5. Determine the BCM Implementation Approach.
6. Initiate the BCM Program
First, determine the BCM Program Injection Point
Not every organization is the same, and not every organization is starting at the same place. BCM is a lifecycle. If you are starting from scratch, the Business Impact Analysis (BIA) is a good starting point within the BCM lifecycle. Maybe your organization has performed a recent BIA/RA and it would be better suited to begin with Plan Development using the Maximum Acceptable Outage (MAO) values, dependencies and technology requirements from the recent BIA/RA results as the basis for the planning strategy.
Next, determine the scope of the Planning effort
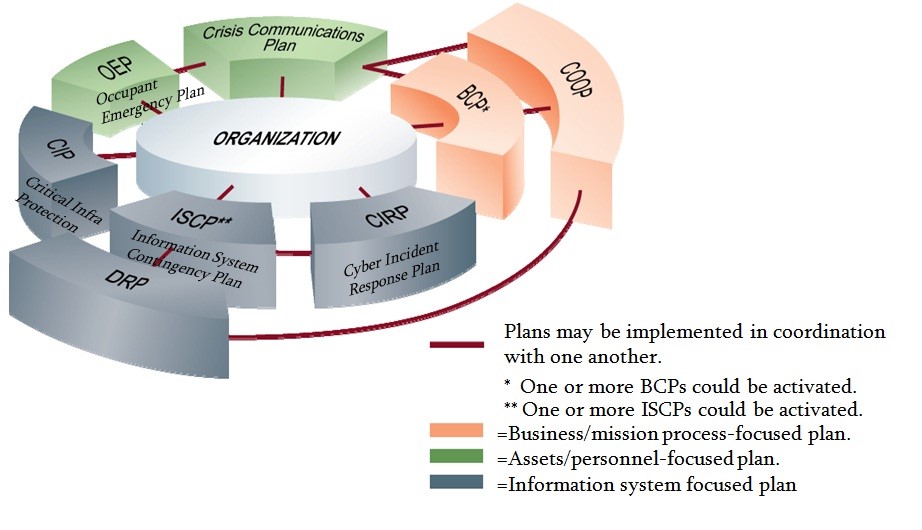
Conduct a review of current Business Continuity Plans. The three main plan types can be described as:
Agency/Business Recovery – Plan development and documentation to resume/recover critical business activities
Crisis Management/Emergency Response – Contingency Planning for executive decision-making, communications and high-level pre-planning activities.
Disaster Recovery– IT Planning Contingency Planning for applications and related infrastructure components (systems, servers, network, databases, etc.)
Your organization may have some or all of these plan types in place already. You may choose to focus first on Crisis Management/Emergency Response first to ensure that effective crisis communications are in place as well as contingencies for safety of people and protection of critical assets during a disruption. Some organizations may choose to prioritize first the resiliency and recovery capabilities of the infrastructure and IT resources with Disaster Recovery planning. Others may need to prioritize the development of operational/business recovery plans for sustaining critical business functions identified during the BIA effort.
All business units, related activities, and associated IT applications and infrastructure must be identified for plan development.
The business units rated as most critical during the Impact Analysis should be the plans documented first by the Business Unit Recovery Teams.
The IT applications rated as most critical during the Impact Analysis should be the plans documented first by the IT Disaster Recovery Teams.
Designate team members that have responsibility for coordinating plan development and documentation.
For more detailed information about how to better prepare your organization with effective BC/DR Planning tools, or to schedule a tabletop exercise with our Certified Business Continuity Professionals, please contact us via:
The contact form using the link at the top of this page
Email at PSISales@ParadigmSI.com
For more information, call us at 800-558-9568 ext. 300
To speak with a Sales Representative about Business Continuity Planning Consulting or Business Continuity Software, please call:814-330-2560
Next up in Part 7: Business Impact Analysis
March 1st, 2023 by ParadigmSI
Implementing a Business Continuity Management Program
1. Establish the BCM Ownership.
2. Align BCM Program to organizational Strategic Goals.
3. Develop the BCM Policy.
4. Determine the BCM Strategy.
The purpose is to address decisions regarding strategies that are not viable to be determined at the individual organizational unit level.
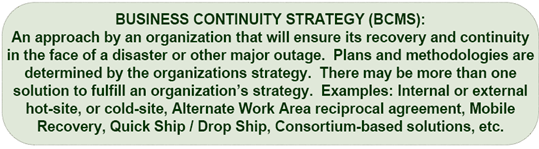
1. Business Continuity Process: The lifecycle of an event:
– COOP-related Procedures (Threat-based SOPs: If fire, dial x###, etc.)
– Crisis Management – (ER/IM: Protect people and assets)
– Business/Disaster Recovery (BRP/COOP: Sustain Critical Functions & IT )
– Resumption (Component of BRP/COOP: Return to Normal Operations)
2. Business Continuity Strategy: Based on loss of asset type:
– Facilities Strategy (hotsite, AWA, etc.)
– Personnel Strategy (remote work, backups, contractors, etc.)
– IT/Systems Strategy (redundancy/Failover, UPS/Gen, etc.)
– Data/Records Strategy (backups, offsite storage, access, etc.)
– Supply Chain Strategy (etc.)
This should be included in the BCP Policy document.
The all-hazards planning approach involves performing a detailed risk assessment of all potential hazards that can possibly affect the organization, and then develop mitigations, planning strategies, and perform testing exercises based on these prioritized hazards. These potential hazards are defined by certain categories, such as Natural Disasters, Human-caused Events, or Technical Disruptions. For each potential hazard, one should determine the rating for each based on the following risk factors:
– Probability of Occurrence (Likelihood the threat will materialize)
– Loss Impact (Direct impact due to the loss of the function)
– Consequence (Downstream losses as a result of the realized threat)
– Exposure (the passive, inherent factors contributing to vulnerability)
– Level of Control (the active, controllable variables to offset vulnerability, e.g. – the Fire Suppression system)
In order to be complete in this assessment, it is also important to understand and consider the other side of the all-hazards planning approach, which is to identify and address all the “asset-types” for the organization that can be impacted by these potential hazards. What are the key assets to the organization, and how can the potential hazards affect these different asset types? In many cases, organizational assets can include: Facilities, Personnel, IT/Infrastructure, and Data/Records. So now, as an example you can develop planning strategies to account for all the “loss of facility” scenarios, whether the cause is fire, flooding, tornado, earthquake, train derailment, or other.
In summary, a comprehensive Enterprise Risk Management strategy will identify all the potential Hazards that can affect the organization, then rank and prioritize these for the different Asset Types that are identified for the organization, and finally employ mitigation strategies, effective planning approaches and testing/exercising to bring the organization into even greater resilience.
For more detailed information about how to better prepare your organization with an All-Hazards Risk Assessment, effective BC/DR Planning tools, or to schedule a tabletop exercise with our Certified Business Continuity Professionals, please contact us via:
– The contact form using the link at the top of this page
– Email at PSISales@ParadigmSI.com
– Call us at 800-558-9568 ext. 300
Next up in Part 5: Determine the BCM Implementation Approach